 ®
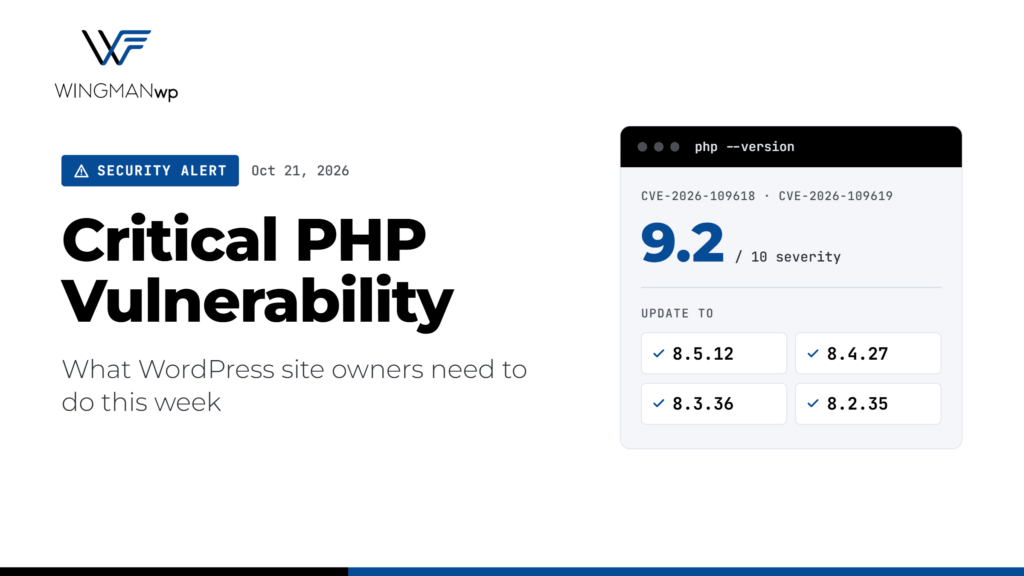
On October 21, 2026, PHP released an emergency security update fixing two critical vulnerabilities in PHP itself. Because WordPress runs on PHP, nearly every WordPress site is affected, and this one needs attention this week rather than at your next scheduled maintenance.
What happened
The two flaws, tracked as CVE-2026-109618 and CVE-2026-109619, are both rated 9.2 out of 10. In plain terms, they can let an attacker run their own code on your web server with a specially crafted request, without logging in or knowing any password.
What makes this especially urgent is the timing. Details leaked before the fix was ready, and attacks were reported on the morning of October 21, before patches were available. The PHP team has also said there is no complete workaround: updating PHP is the only safe option.
The fixed versions are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Sites running PHP 8.1 or older receive no fix at all and should move to a supported version.
Why updating WordPress won’t fix it
This isn’t a WordPress or plugin bug. PHP is the language that runs underneath WordPress on your server, so a fully updated WordPress site can still be exposed if PHP is outdated. The flaw can even be triggered before WordPress loads, which means security plugins inside WordPress can’t reliably block it.
This is the part of maintenance that often slips through the cracks. Plugin updates show up in your dashboard; PHP updates usually don’t.
What to do now
- Check your PHP version under Tools > Site Health > Info > Server in your WordPress dashboard.
- Ask your host to confirm your server is on the patched release. Many hosts are rolling it out automatically, but get a clear answer rather than assuming.
- Update PHP yourself if you manage your own server, and restart PHP-FPM or Apache so the new version actually loads.
- Test your site after the update, including key pages, contact forms, checkout and login areas.
- Watch for warning signs such as unfamiliar admin users, unexpected file changes or unusual traffic since October 21.
If your site handles patient records, payments or customer accounts, don’t wait. A server-level breach can quickly become a compliance issue as well as a technical one.
How WingmanWP can help
We treat websites like infrastructure, which means looking after the full server stack, not just plugins. For the sites we manage, we confirm patches directly with hosts and roll out updates through a tested release process so security fixes don’t cause new problems.
Not sure where your site stands? Contact WingmanWP and we’ll check your PHP version and patch status, and tell you plainly whether you need to act.
Sources: PHP 8.5.12 release notes, Codeable
 Ayesha UmarWritten by